

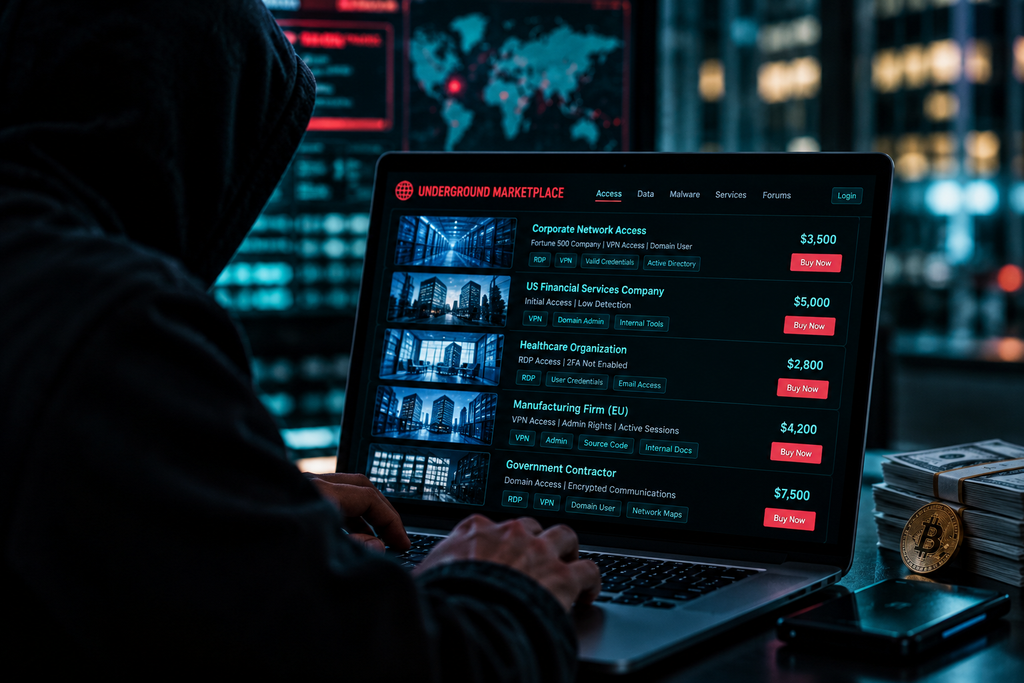
Someone Is Selling Access to Your Company’s Network: Inside the Underground Market for Corporate Access
Your company hasn’t reported a cyberattack. Employees are working normally. The servers are running. Yet somewhere online, a stranger claims they can give a buyer access to your business network.
The advertisement is short.
“Corporate network access available. Established company. Remote access. Serious buyers only.”
There is no company logo, no leaked database, and no ransom demand.
Just a description of an organization, a claim about access, and a price.
To an ordinary reader, it might look like another suspicious online advertisement.
To a cybersecurity investigator, it raises a much more serious question:
Has someone already gained access to the company’s systems—and are they now attempting to sell that access to another criminal?
This is the world of initial access brokers, an underground cybercrime activity in which individuals advertise unauthorized access to business systems.
For the affected company, the consequences can be significant.
An attacker who purchases genuine access may attempt to steal confidential documents, compromise additional accounts, disrupt operations, or prepare a ransomware attack.
The organization may have no idea that its security has already been breached.
At Cyb3rsect, our digital investigation content examines how suspicious account activity, compromised systems, and electronic evidence can help organizations understand potential security incidents.
This article explores what initial access brokers do, how corporate access can become a criminal commodity, and how investigators assess whether a company is genuinely at risk.
The Cyberattack That Starts Before the Attack
Most businesses imagine a cyberattack beginning when something goes visibly wrong.
A computer displays a ransom message.
Employees lose access to company files.
Customer records appear online.
An administrator notices unusual activity.
But a serious incident can begin long before these events.
An attacker may obtain valid account credentials and wait.
A compromised remote access account may remain usable without attracting immediate attention.
An exposed administrative interface may provide a route into the environment.
Some attackers seek to exploit that access themselves.
Others attempt to sell it.
This creates a separation between the person who initially compromises an organization and the person who eventually conducts a more damaging attack.
A business might therefore face several stages of malicious activity involving different actors.
Understanding that distinction is essential when reconstructing an incident.
Who Are Initial Access Brokers?
An initial access broker, commonly abbreviated as IAB, is a threat actor who obtains or advertises unauthorized access to computer systems and offers that access to other criminals.
The access being advertised might involve a corporate account, remote access service, cloud environment, or another entry point into an organization’s infrastructure.
Some sellers claim to possess access to large enterprises.
Others advertise smaller organizations.
The listings may describe the target’s industry, location, revenue range, or type of access.
However, these claims are not independently verified simply because they appear in a marketplace.
Some sellers exaggerate their capabilities.
Others advertise expired credentials, previously exposed systems, or entirely fabricated access.
A criminal listing is an investigative lead—not proof that the advertised organization has been compromised.
Why Would Someone Sell Access Instead of Stealing Data?
Different cybercriminals have different objectives and capabilities.
An individual may know how to obtain credentials but lack the resources or interest to conduct a larger intrusion.
Another criminal group may specialize in extortion, ransomware, or data theft.
Selling access allows the first actor to monetize an opportunity without carrying out the later stages of an attack.
This creates an underground division of labor.
The access seller focuses on obtaining or maintaining entry.
The buyer may attempt to exploit that entry for financial gain.
For defenders, the important point is that an apparently minor account compromise can create opportunities for more serious activity.
What Types of Corporate Access Are Advertised?
The exact content of an underground listing varies.
Commonly described categories include:
Remote Access Accounts
Credentials associated with services that allow authorized users to connect to business environments remotely.
VPN Accounts
Accounts associated with virtual private network services used by employees or contractors.
Cloud Accounts
Access to business applications, cloud management interfaces, or hosted resources.
Administrative Accounts
Accounts that may possess elevated permissions.
Compromised User Credentials
Usernames, passwords, or other authentication material allegedly associated with a business.
Access Through Third-Party Services
An attacker may claim access through a supplier, contractor, or service provider connected to the organization.
These categories are not equivalent.
A single ordinary user account does not necessarily provide broad network control.
Likewise, a seller’s claim of administrator access does not establish that the claimed privileges exist.
Investigators must determine what access, if any, can actually be substantiated.
The Company That Was Listed for Sale
Consider a hypothetical logistics company with several regional offices.
The organization uses cloud email, remote employee access, and a central business management platform.
One morning, its security team receives a notification from an external threat intelligence provider.
An underground advertisement appears to describe the company.
The listing claims to offer remote access to a logistics business operating in the same country and revenue category.
The advertisement does not identify the company directly.
However, several characteristics appear to match.
Management immediately fears that an attacker has entered the network.
But the evidence remains incomplete.
The description could apply to numerous organizations.
The seller might be exaggerating.
The alleged access could belong to a third-party vendor.
It might even be an old account that has already been disabled.
An effective investigation begins by testing the allegation against authorized internal records.
The organization reviews relevant authentication activity, remote access accounts, privileged users, and recent security events.
It does not need to purchase the advertised access or communicate directly with the seller to begin assessing its own exposure.
This distinction is important.
A credible security response relies on lawful, independently verifiable evidence.
How Do Criminals Obtain Corporate Access?
There is no single pathway.
Unauthorized access can result from several types of security failures.
Stolen credentials: An attacker obtains authentication information through phishing, malware, previous breaches, or other means.
Account takeover: A legitimate business account becomes controlled by an unauthorized person.
Unpatched vulnerabilities: A security weakness in an exposed service or application is exploited.
Misconfigured services: Systems are unintentionally accessible in ways that create security risks.
Compromised third parties: Access associated with a vendor or contractor becomes a pathway into a connected organization.
Insider misuse: Someone with legitimate permissions may improperly disclose or use access.
Each possibility requires a different investigative approach.
A suspicious login does not automatically prove credential theft.
A vulnerable system does not establish that exploitation occurred.
And a criminal advertisement does not prove that the seller successfully entered the environment.
The Employee Account Nobody Disabled
One overlooked security problem is incomplete employee offboarding.
A departing employee may lose access to their primary company account while retaining access to a separate application.
The organization might also overlook shared credentials, long-lived sessions, or integrations created during employment.
If those access paths remain active, they can create security risks.
However, the existence of a former employee’s active account does not prove misconduct.
An attacker may have obtained the credentials independently.
An automated integration may still be using the account.
Investigators must distinguish an access-control failure from evidence of unauthorized use.
This issue is closely connected to corporate investigations involving employee misconduct and digital evidence.
Why a Stolen Password May Be Only the Beginning
A compromised password can create several potential risks.
The affected account may provide access to email, business applications, or confidential documents.
In some environments, the account may also be associated with additional permissions or services.
However, the impact depends on the account’s actual privileges and the organization’s security controls.
Multi-factor authentication, conditional access policies, session management, and other safeguards may prevent a stolen password from being sufficient for entry.
An investigation should establish whether the credentials were merely exposed or whether unauthorized authentication actually occurred.
Those are different findings.
Can Your Company Be Compromised Without Any Malware?
Yes.
Some unauthorized access incidents involve legitimate accounts and ordinary business applications.
An attacker using a compromised account may interact with systems through their normal interfaces.
For example, suspicious activity might involve unexpected cloud sign-ins or unusual document access.
No malicious executable is necessarily required.
This can make investigation more difficult when an organization focuses exclusively on antivirus alerts.
Authentication records, cloud audit logs, and account activity may be more relevant than malware detection in certain incidents.
For a closer look at these evidence sources, read Cyb3rsect’s Cloud Forensics: Investigating Cloud Accounts, Audit Logs, and Digital Evidence.
What Happens After Corporate Access Is Sold?
The consequences depend on whether the access is genuine and what the buyer attempts to do.
Potential outcomes include unauthorized account activity, confidential information theft, business email compromise, and operational disruption.
In some incidents, an attacker may attempt to expand access beyond the initial account.
Other cases may involve attempts to deploy ransomware or threaten the publication of stolen information.
However, a listing does not mean that any of these outcomes has occurred.
An organization should investigate the exposure without assuming that every possible consequence has already happened.
The priority is to determine whether unauthorized access exists and whether it remains active.
The Difference Between an Underground Claim and a Confirmed Breach
Suppose an advertisement claims that a manufacturing company has been compromised.
What would establish that the claim is credible?
The answer depends on the evidence.
A listing containing only an industry and country is relatively weak.
A listing containing accurate, nonpublic details may justify closer examination.
Even then, the information could have come from an older incident, a vendor, or another source.
Stronger evidence may emerge when authorized internal records show suspicious activity corresponding to the allegation.
For example, an organization may identify unauthorized access to a remote service during the relevant period.
The investigation can then assess whether the activity is consistent with the advertised claim.
But investigators should not treat correlation as automatic proof that a particular seller was responsible.
How Investigators Examine Suspected Network Access Sales
A structured investigation may proceed through several areas of evidence.
Establish What Was Advertised
Document the available listing details, dates, descriptions, and relevant claims.
Evidence should be collected through lawful and authorized means.
Determine Whether the Organization Matches
Compare the advertised characteristics with the company’s actual systems and operations.
Avoid assuming that a broad description identifies a particular company.
Review Authentication Records
Examine available sign-in logs, unusual access patterns, and relevant account activity.
Examine Remote Access Services
Determine whether unexpected connections or account activity occurred.
Review Privileged Accounts
Assess whether elevated permissions were used in suspicious circumstances.
Examine Cloud Activity
Look for relevant security events, unusual access, or changes to account settings.
Correlate Endpoint and Network Evidence
Where available, device and network records may help reconstruct suspicious activity.
Assess Whether Exposure Is Ongoing
Determine whether compromised accounts, unauthorized sessions, or vulnerable services still create risk.
The investigation should produce a timeline and distinguish confirmed findings from unresolved questions.
Five Questions an Investigator Should Answer
A company responding to a suspected access sale needs more than a statement that its name appeared online.
The investigation should aim to answer:
- Is there credible evidence of unauthorized access?
- Which accounts, services, or systems may be affected?
- When did the earliest confirmed suspicious activity occur?
- Is there evidence of additional access, data exposure, or other malicious activity?
- What actions are necessary to contain the risk and preserve evidence?
These questions focus the investigation on decisions that matter to the organization.
What Digital Evidence Can Reveal
Several records may be relevant.
| Evidence source | What it may help establish |
|---|---|
| Identity provider logs | Relevant sign-ins and authentication events |
| VPN records | Connections associated with remote access accounts |
| Cloud audit logs | Account activity, permission changes, and resource access |
| Endpoint telemetry | Relevant device and application activity |
| Network records | Available connection patterns and suspicious communications |
| Administrative logs | Changes involving privileged accounts or system configuration |
| Email records | Related phishing, account compromise, or suspicious communications |
Not every organization retains all of these records.
Some systems have limited logging.
Others overwrite older events after a defined retention period.
This is one reason early evidence preservation matters.
Can Investigators Identify the Person Selling Access?
Sometimes investigators can identify technical indicators associated with a suspected intrusion.
However, identifying the individual responsible is much more difficult.
A seller may use a pseudonym.
The access may have passed between multiple people.
Compromised accounts and intermediary infrastructure can obscure the origin of activity.
An IP address does not automatically identify a person.
A marketplace username does not establish a real-world identity.
Reliable attribution may require evidence and legal processes unavailable to a private organization.
A professional investigation should explain these limitations.
Why Buying the Advertised Access Is Not a Safe Solution
A company that discovers a suspicious listing may be tempted to purchase the access to determine whether it is genuine.
This can create legal, financial, and operational risks.
The seller may be a fraudster who possesses nothing.
The transaction may expose the company to further extortion or malicious content.
Purchasing unauthorized access can also raise serious legal concerns.
Organizations should coordinate their response with qualified incident responders, legal counsel, and relevant authorities rather than attempting to negotiate independently with criminal sellers.
An internal security investigation can begin without buying anything.
What Should a Company Do If Its Network Access Is Advertised?
The first response should be proportionate to the available evidence.
Preserve the alert. Retain the source information, relevant timestamps, and the exact claims made.
Notify the security team. Ensure that authorized incident responders assess the report.
Review exposed services and accounts. Examine relevant authentication records and remote access configurations.
Contain confirmed unauthorized access. Revoke suspicious sessions, disable compromised accounts, or apply other appropriate controls.
Preserve forensic evidence. Avoid unnecessary cleanup that could destroy relevant records.
Assess potential data exposure. Determine whether there is evidence that sensitive information was accessed or transferred.
Coordinate legal and reporting decisions. Consider applicable contractual, regulatory, and law enforcement requirements.
Continue monitoring. Look for additional suspicious activity while the investigation proceeds.
If active compromise is confirmed, containment may need to happen immediately while evidence preservation is coordinated.
The Cost of Waiting for a Ransom Note
One of the most dangerous assumptions is that a business will know when an attacker gains access.
Unauthorized access may remain unnoticed for some time.
A company that waits for ransomware, data theft, or visible disruption may miss an opportunity to investigate earlier warning signs.
This does not mean every security alert represents an emergency.
False positives and unsubstantiated claims occur.
But credible indications of unauthorized access should be assessed promptly.
The purpose of early investigation is to determine whether the threat is real and reduce the opportunity for additional harm.
When the Problem Starts With a Third-Party Vendor
Modern businesses depend on external service providers.
A contractor may have remote access to company systems.
A software provider may operate integrations connected to business applications.
A managed service provider may administer part of the environment.
If a third party’s credentials or systems are compromised, connected organizations may face exposure.
However, the existence of a vendor relationship does not establish that the vendor caused an incident.
Investigators should examine the specific permissions, connections, and available records.
Relevant contracts and incident notification arrangements may also need review.
How to Preserve Evidence Before It Disappears
Digital evidence can be lost through routine system activity.
Authentication logs may expire.
Cloud records may be retained for limited periods.
Endpoint activity may be overwritten.
A hurried cleanup may also remove information needed to reconstruct the incident.
Evidence preservation should therefore be part of the response.
Depending on the environment, this may include exporting relevant logs, documenting suspicious sessions, preserving affected device records, and recording administrative actions.
The organization should maintain appropriate access controls and chain-of-custody documentation.
For a practical explanation, see Cyb3rsect’s Digital Evidence Preservation: How to Preserve Digital Evidence for Cybercrime and Fraud Investigations.
Can a Company Prevent Its Network Access From Being Sold?
No organization can guarantee that credentials or access will never be exposed.
However, businesses can reduce the likelihood and impact of compromise.
Important controls include phishing-resistant authentication where practical, timely security updates, restricted remote access, privileged account management, and regular access reviews.
Organizations should also remove unnecessary accounts, monitor authentication events, and review third-party permissions.
Sensitive systems should not be accessible through accounts with more privileges than necessary.
Incident response planning is equally important.
A business should know how to investigate suspicious access, preserve evidence, and contain confirmed compromises.
What a Corporate Network Access Investigation Report Should Contain
A useful report should not simply repeat the underground advertisement.
It should explain the allegation, the evidence examined, and the findings.
Relevant sections may include:
- Incident background and investigation scope
- Description of the suspected access sale
- Systems and accounts examined
- Evidence sources and preservation methods
- Timeline of relevant events
- Confirmed security findings
- Potential impact and unresolved questions
- Containment and remediation recommendations
- Investigative limitations
A report may conclude that unauthorized access was confirmed.
It may instead find that a claim could not be substantiated.
Both outcomes can be valuable when clearly supported by evidence.
For related guidance, see Digital Forensic Report: What a Professional Forensic Report Should Contain.
How Cyb3rsect Approaches Suspected Corporate Network Compromise
At Cyb3rsect, corporate cybersecurity investigations are approached through the examination of available digital evidence.
A suspected network access sale may require analysis of authentication activity, remote access records, cloud services, relevant devices, and security alerts.
The investigative objective is to determine whether unauthorized access can be established, what systems may be affected, and whether the exposure remains active.
Where appropriate, the findings can help an organization prioritize containment and security improvements.
The investigation should not promise to identify every criminal involved or guarantee that all unauthorized access can be reconstructed.
Technical findings must reflect the available evidence.
Organizations seeking information about digital forensics, corporate cyber investigations, and suspicious account activity can explore Cyb3rsect.
Final Thoughts: Your Company Could Be the Product
The underground trade in corporate access reveals an uncomfortable reality about modern cybercrime.
Sometimes the first objective is not to steal money or encrypt files.
It is simply to obtain entry.
That access may then be advertised to someone with a different criminal objective.
For businesses, the challenge is recognizing that an apparently ordinary account compromise can create broader risks.
A suspicious marketplace listing should not be accepted as proof of a breach.
But it should not be dismissed without appropriate assessment when credible evidence points to the organization.
The most useful response is an investigation that establishes what can be verified, protects relevant evidence, and addresses confirmed security weaknesses.
The question is not merely whether someone claims to have access to your network. It is whether the evidence shows that they do—and what your organization can do before the situation becomes more serious.
For further reading about corporate cybersecurity, account compromise, and digital investigations, visit Cyb3rsect.
